Poltergift

A secret gift exchange on the Tari Ootle where nobody, not even the chain, knows who gave what to whom.

  1. Open a haunted round (5 × 5 tTARI)
  2. Each ghost drops a gift
  3. Round sealed: gifts possessed
  4. Ghosts claim in random order
  5. Every ghost holds one gift

Press Summon 5 Ghosts: a full round runs in your browser in about 15 seconds.

👁 Observer

What the explorer shows anyone.

🎁 Recipient

Pick a ghost: only its own gift opens.

🧮 Auditor

Totals only, from public data.

🧪 Attack lab

Each attempt runs against a copy of this round through the same rules the on-chain template enforces (CI replays them against the real template).
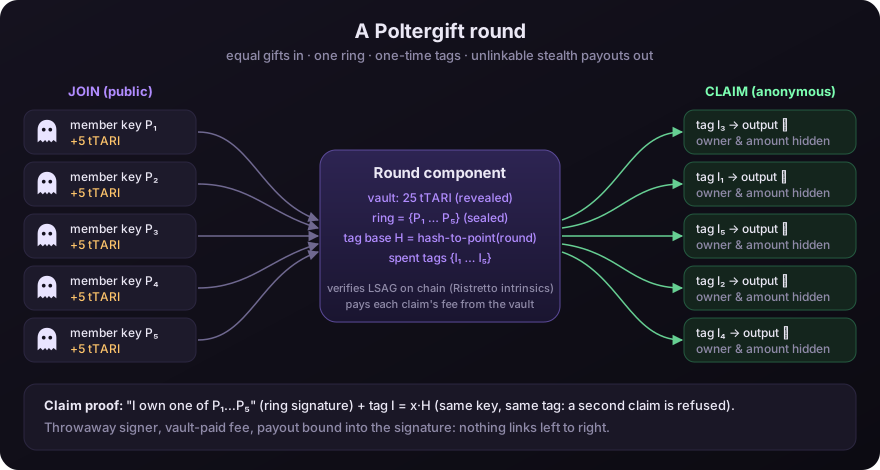
    Deposits go into a round vault under N member keys; claims come out to fresh stealth outputs proven only by a ring signature and a one-time tag.

    How it works

    1. Join. Each ghost makes a fresh member key for this round and drops exactly one gift (same amount for everyone), ideally paid from a stealth coin so no account appears.
    2. Seal. When the round is full, the template fixes the ring of member keys.
    3. Claim. A ghost proves "I am one of the members" with a linkable ring signature (LSAG over Ristretto255), verified on chain with native intrinsics. Its key image I = x·H is a one-time tag: a second claim by the same ghost reuses the tag and is refused. The signature commits to the exact payout output, so nobody can redirect it.
    4. Payout. The gift goes to a brand-new stealth output; the claim transaction is signed by a throwaway key and its fee is paid by the round vault, so it points at nobody.
    5. Refund. If the round never fills, or a ghost vanishes, a deadline lets depositors take their gift back. The refund proves the depositor's tag is unspent, so nobody can both claim and refund.

    What still leaks (membership, timing, equal amounts by design) is listed honestly in THREAT_MODEL.md.

    Source, tests and threat model on GitHub →